
We help you build it.
Requirements, ownership, evidence, and the people who run the program.
Certification is a milestone. Building a management system that lasts is the goal.
ISO/IEC 27001 certification provides independent validation that an organization has established and operates an information security management system that meets the requirements of the standard.
For many organizations, certification is also becoming increasingly important to customers, partners, insurers, investors, and other stakeholders who want confidence that information security is being managed systematically.
Trygg helps organizations build the management system behind that certification.
Our role is to help you understand the requirements, put them into practice, establish ownership, connect evidence, prepare your people, identify gaps, and operate the program.
The independent certification body makes the certification decision.
That distinction matters.
Requirements, ownership, evidence, and the people who run the program.
The certification body decides whether it meets the standard.
Trygg was built around practical experience implementing and operating information security management systems.
Our leadership includes Certified ISO/IEC 27001:2022 ISMS Lead Implementer expertise, providing formal training and qualification in implementing management systems aligned with the requirements of ISO/IEC 27001.
Credentials alone are not what make an implementation successful.
The harder part is translating a standard into something that makes sense inside a real company.
Those are the questions Trygg was built to help answer.
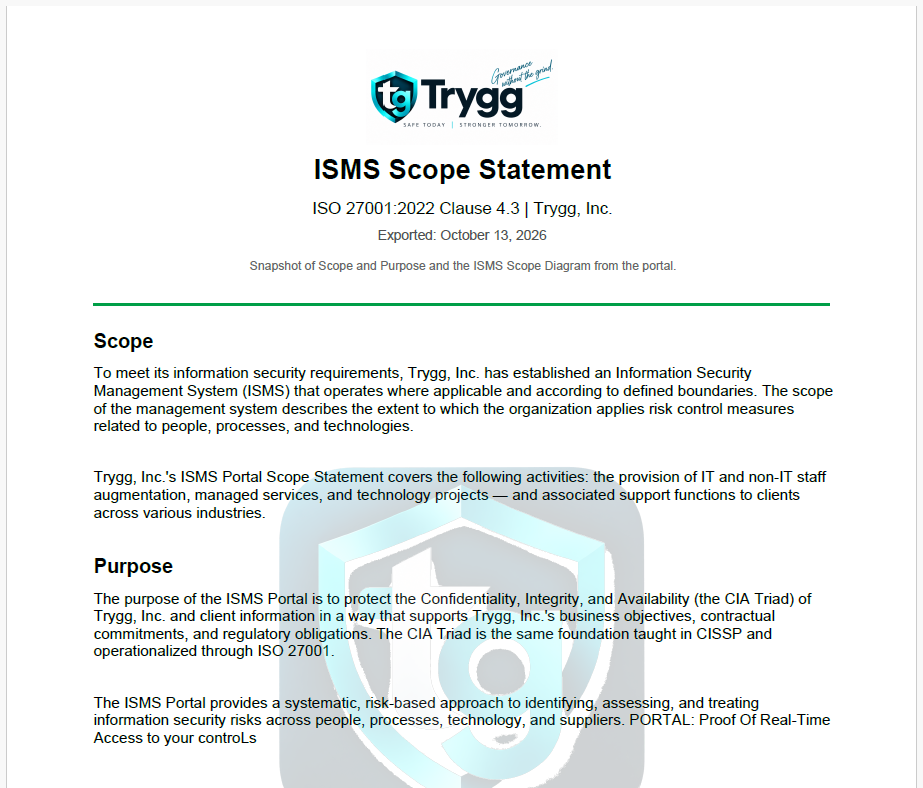
ISO/IEC 27001 tells an organization what its information security management system needs to accomplish.
Every organization still has to determine how those requirements apply to its own business. Trygg helps make that translation practical.
We work with your organization to understand scope, interested parties, risks, objectives, policies, processes, controls, responsibilities, evidence, management review, corrective action, and continual improvement.
The result should feel like YOUR management system, not ours.
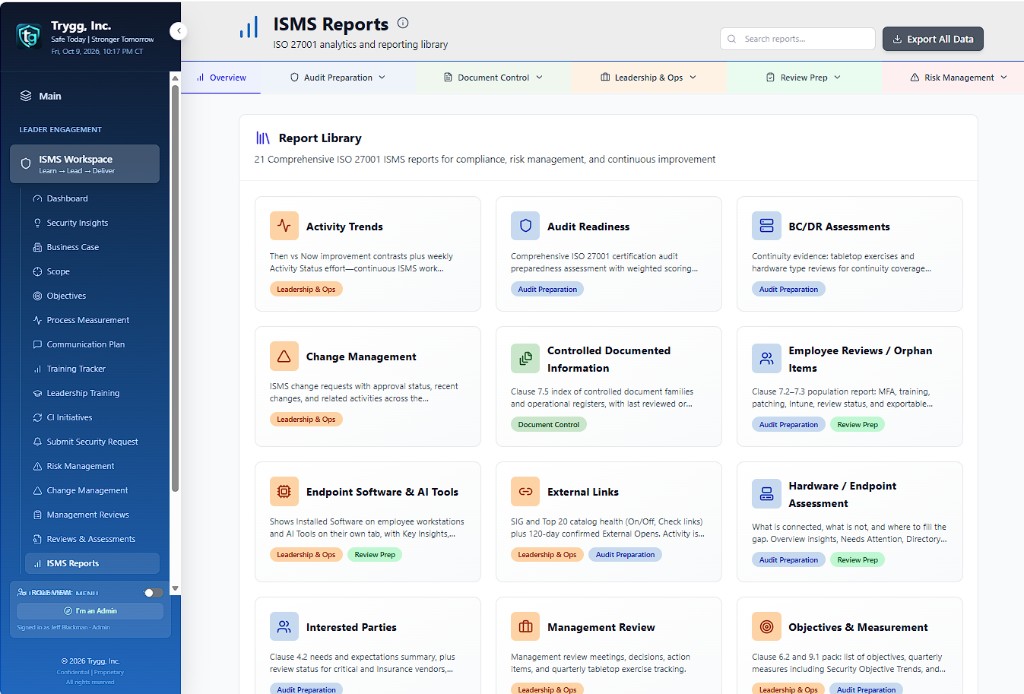
Certification readiness is built throughout the engagement, not during the final few weeks.
As the management system develops, Trygg helps your organization understand what is ready, what remains open, where evidence exists, and where additional work is needed.
That includes preparing the organization for the questions an auditor is likely to explore.
Leadership should be able to explain the management system. Control leaders should understand their responsibilities. Processes should reflect what people actually do. Evidence should support those processes. Risks and objectives should be current. Management review should demonstrate leadership involvement. Corrective actions should show that issues are identified and addressed.
By the time the certification audit begins, these should not be new concepts. They should be part of how the organization operates.
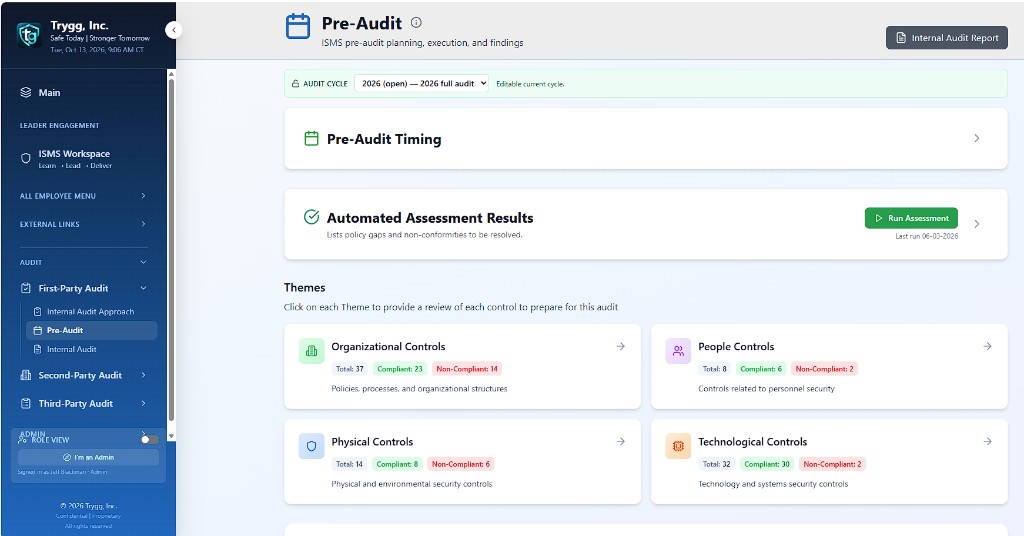
Before the certification process begins, we review the management system as a whole.
We look for gaps between what the organization says it does and what can actually be demonstrated.
We review scope, risks, objectives, policies, processes, controls, evidence, ownership, training, management activities, and other elements of the management system.
The purpose is simple.
Find the questions before the auditor does.
More importantly, find the answers while you still control the timeline.
An internal audit is not simply another requirement to complete before certification. It is an opportunity to challenge the management system.
The value of the internal audit is not proving that everything is perfect. The value is discovering where improvement is needed before the external certification audit and using those findings to make the management system stronger.
ISO/IEC 27001 is a management system. That means leadership has a role beyond approving a policy or funding a project.
Trygg helps bring the information leadership needs into a forum they can actually use:
Management review becomes an opportunity to understand the security program and make decisions about it, rather than another meeting created solely to satisfy an audit requirement.
Leadership involvement is one of the most important differences between having an ISO program and operating one.
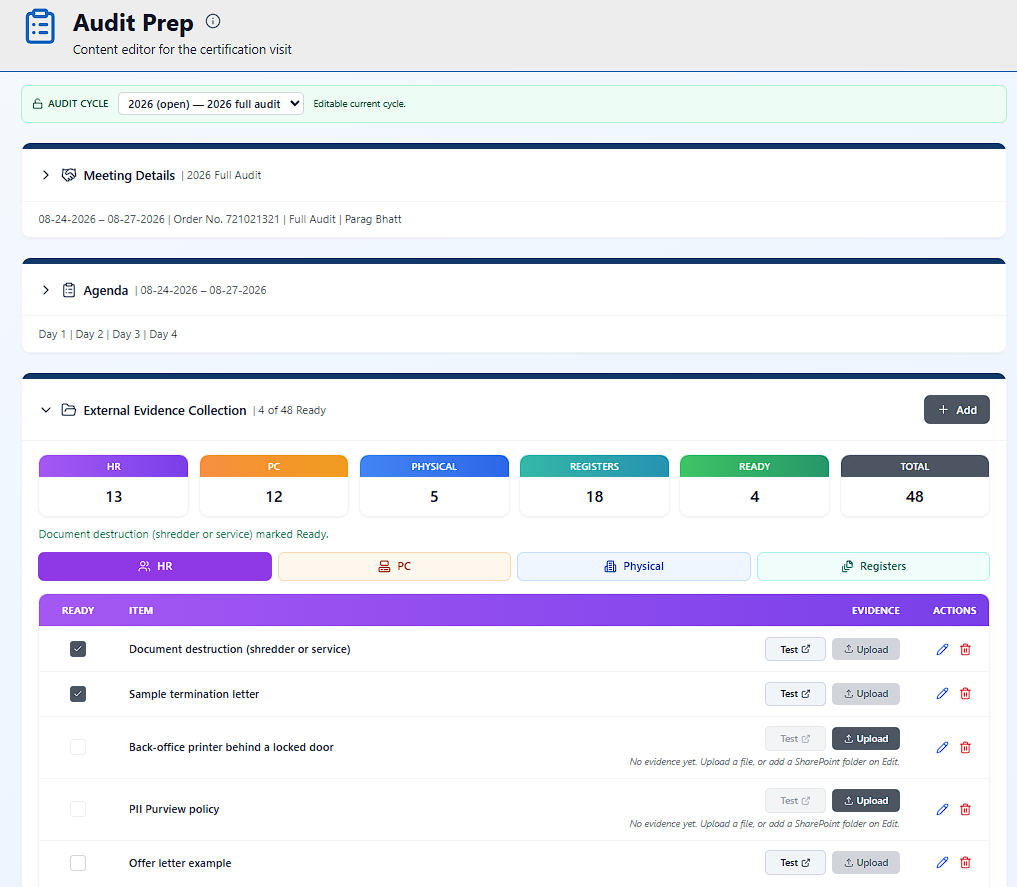
Before your certification auditor arrives, we walk through the management system again. We make sure open items are visible rather than hidden. An AI assisted pre-audit analysis identifies gaps and suggested remediation steps.
We review the evidence path. We address remaining questions. We work with control leaders so they understand their responsibilities and are comfortable explaining the processes they actually perform.
We help leadership understand what may be asked of them and why. We are not preparing people with scripted answers.
We are helping them understand their own management system well enough that scripts are unnecessary.
The certification auditor must remain independent.
Trygg does not control the audit, determine findings, or guarantee certification.
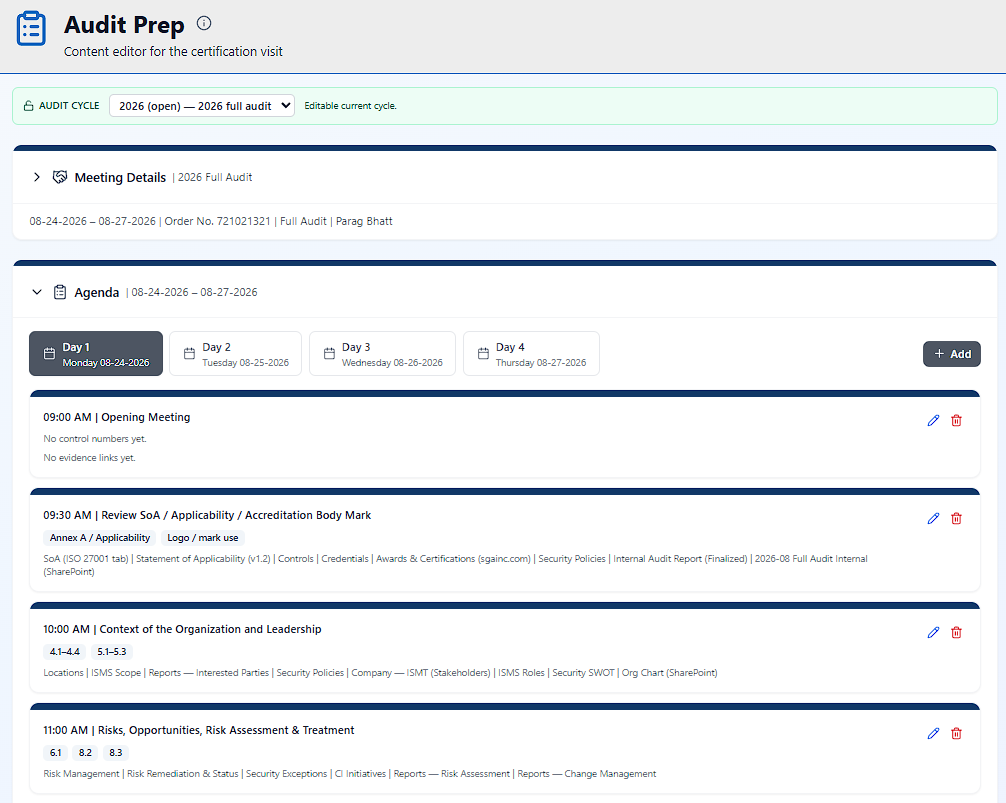
What we can do is help make sure the management system and supporting evidence are organized, understandable, and accessible.
When appropriate within the audit process, we can also remain available to support your team with the Trygg environment and help locate the information and evidence being requested. We built a custom auditor role that allows them to see only what they need to streamline the audit, the evidence, and the results.
When the auditor asks for proof, your team should not be starting the search. They should be opening the control.
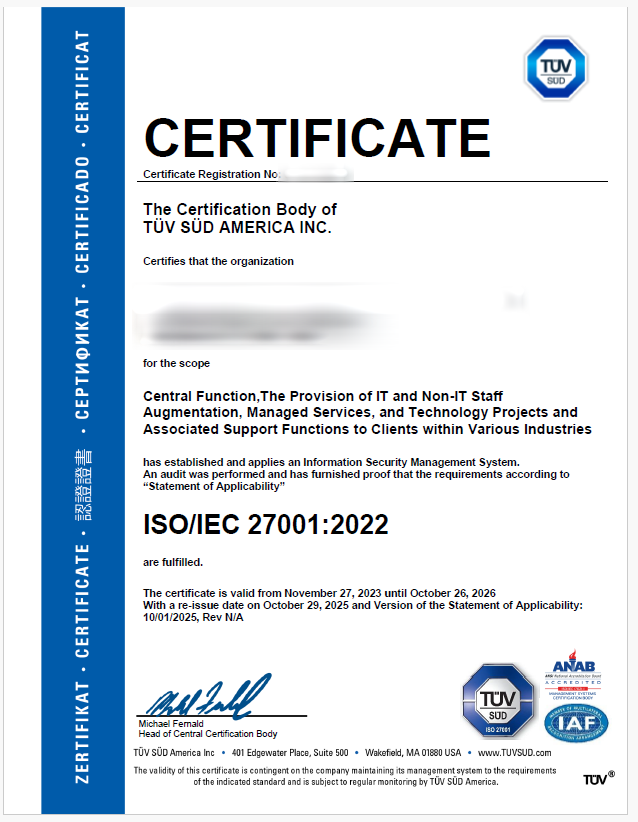
Once certification is achieved, the management system keeps operating.
Controls still need owners. Evidence still needs to remain current. Risks change. Objectives need to be measured. Employees need training. Technology changes. Management reviews continue. Internal audits continue. Corrective actions need to be addressed.
Future surveillance and recertification audits will test whether the system continues to operate.
That is one reason Trygg is designed as an ongoing management system rather than a certification project.
We want to help you reach certification.
Then we want to help make maintaining it considerably less difficult than earning it the first time.