Solutions

  1. Build
  2. Operate
  3. Audit
  4. Certify
  5. Improve
  6. Surveillance
  7. Continue

More than software. More than consulting.

Trygg combines technology, implementation, and ongoing support to help organizations build an ISO/IEC 27001 management system they can actually operate.

The portal gives you the structure. Our engagement helps you put that structure into practice. Together, we define scope, understand risk, establish ownership, build the processes, connect operational evidence, prepare your people, and get the management system ready to be tested.

But certification is not the finish line. Our goal is not to hand you software and wish you luck.

A successful ISO/IEC 27001 program also requires leadership adoption, control owner participation, ongoing evidence, management review, corrective action, and continual improvement.

Our goal is to help you build a management system your organization understands, your leadership uses, and an auditor can follow.

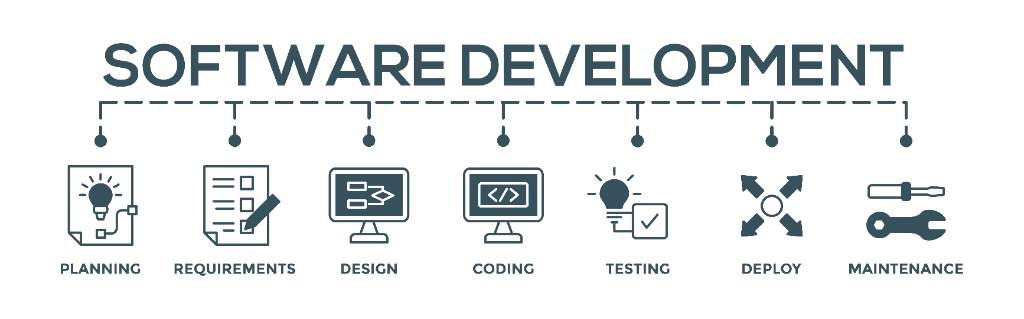
Software development steps from planning through maintenance

One solution. Three responsibilities.

Implement

We start by helping you build the management system correctly.

Through a structured, time bound engagement, we work with your team to establish scope, assess where you are today, identify gaps, organize risks, develop or update policies and processes, assign ownership, and configure Trygg around how your organization actually operates.

Where practical, we connect Trygg to the technologies already responsible for identity, email, endpoints, backups, and other security functions.

The result is not a generic ISO program.

It is your management system, built around your business.
A path from 2026 through plan, action, and goals to 2027.

Prepare

Being ready for an audit means more than having the right documents.

Your leaders need to understand their responsibilities. Evidence needs to support what your policies and processes say is happening. Risks and objectives need to be current. Management review needs to mean something. Open issues need owners.

We work with your team to make sure the program is not only documented, but understood and operating.

Then we walk it the way an auditor will.

Questions become easier to answer because the organization is not memorizing answers for an audit. Your people are explaining the system they already use.

A winding road through green forest, seen from above

Support

After implementation, the management system becomes part of how you operate.

That is when support matters most.

We stay engaged to help maintain the platform, integrations, automation, and processes you depend on. We help answer questions, work through changes, identify issues, prepare for upcoming reviews, and keep the program moving forward.

When something changes in your business or technology environment, the management system should change with it.

Support is not an afterthought.

It begins with how we build the solution.

Colleagues standing together with arms linked

Built for certification. Designed for adoption.

Passing an audit is an important milestone. Leadership adoption is what makes the program sustainable.

A CEO or COO should not need to become an ISO expert to understand whether the organization is doing what it says it does. Control leaders should not need to search through a standard to understand what they own. The person managing the program should not need a collection of spreadsheets to determine what is current.

Trygg gives each of them a view of the same management system. Leadership sees risk, performance, accountability, and areas requiring attention.

Control leaders see what they own, the process they are responsible for, and the evidence supporting it. The program lead sees how the pieces come together.

The auditor follows that same path. That is how ISO/IEC 27001 moves from a compliance project to part of how the company operates.

A team reviewing results together in a glass meeting room.

Technology that connects to reality

Your security program already depends on technology. Trygg does not need to replace it.

Instead, we connect the management system to the technologies already performing important security functions. Identity, email, endpoints, backups, and other systems can provide operational evidence that helps demonstrate whether controls are actually working.

This changes the conversation. Instead of asking only, “Do we have a policy for this?” you can begin asking, “Is this actually happening?”

Instead of relying entirely on evidence collected for the audit, leadership can see when operational information was last refreshed. The management system becomes closer to the systems it is supposed to govern.

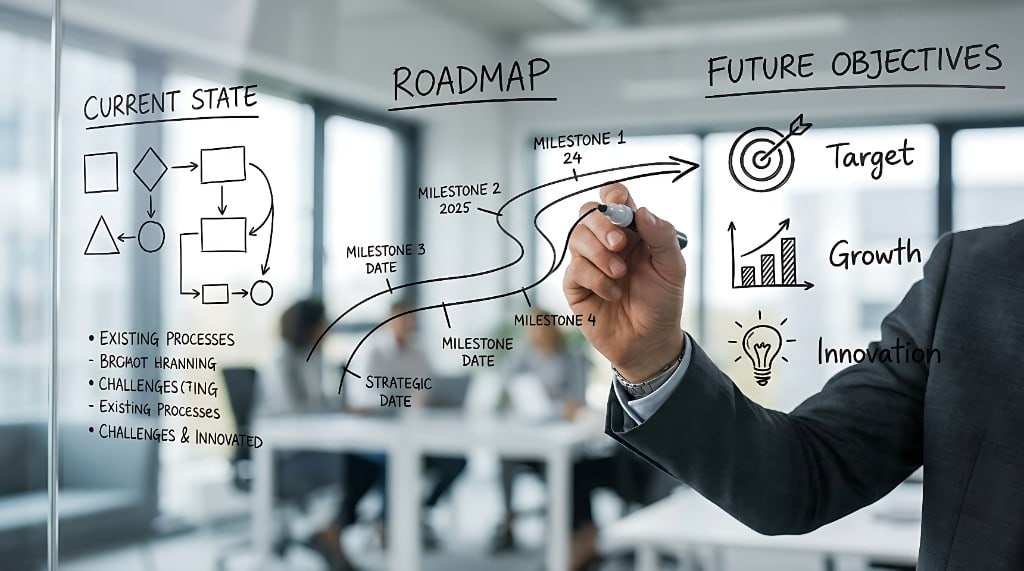
A hand drawing a roadmap from the current state toward future objectives.

People still matter

Automation can tell you a great deal. It cannot own a control.

Every control ultimately depends on people understanding what is expected of them and taking responsibility for the result.

That is why Trygg assigns ownership and connects controls to the people, processes, and evidence behind them.

During implementation, we work with control leaders to make sure they understand what they own, why it matters, and how their responsibilities are demonstrated.

Leadership adoption starts there. The security program stops belonging to one compliance person and becomes a responsibility shared across the organization.

A team reviewing results together around a meeting table.

The audit should confirm what you already know

Audit preparation should not begin with a search for evidence. By the time your certification audit arrives, the management system should already be telling you where you stand.

We help you review the program the way an auditor will see it. Scope, risks, controls, objectives, processes, evidence, training, management review, corrective actions, and open items are examined together.

Where something is not ready, you know. Where evidence is missing, you know. Where ownership is unclear, you know.

The goal is not to make the organization look ready for a few days. The goal is to make it ready because the system is actually operating.

Two colleagues reviewing information together on a tablet.

After certification

The certificate is a milestone. The management system continues.

Risks change. Employees change. Technology changes. Customers ask new questions. Controls need attention. Evidence needs to remain current. Management reviews continue. Surveillance audits arrive.

Trygg remains the place where that work comes together. Our ongoing relationship helps you maintain what was built, adapt it as your organization changes, and prepare for what comes next.

You should not have to rebuild your ISO program every time an audit appears on the calendar. You should already be running it.

Colleagues shaking hands in a glass meeting room after a review.

What success looks like

At the end of the engagement, success is not measured by the number of documents we created. Your organization knows what is in scope, leadership can see where the program stands, and control leaders know what they own.

Risks have owners and actions. Policies reflect how the company actually operates. Evidence supports what the organization says it is doing, and the portal is being used.

The organization is prepared for its certification audit, and after the audit is over, the management system keeps working. That is the solution.

A leadership team talking together in a bright office.

Implement it | Operate it | Prove it | Improve it